
Error: is not authorized to perform dynamodb:* on resource
Answered by Rafal Wilinski
What's Causing This Error
This error occurs when the IAM Role associated with the service performing a DynamoDB operation does not have the required permissions.
For example, this error would get thrown if a Lambda function does not have permission to perform a query operation and executes a query.
Solution - Here's How To Resolve It
To resolve the error, you will have to bind the required policy to the IAM Role of the service.
First, visit the IAM Console and search for the role that needs the DynamoDB policies. For example, the role that is bounded to the Lambda function.
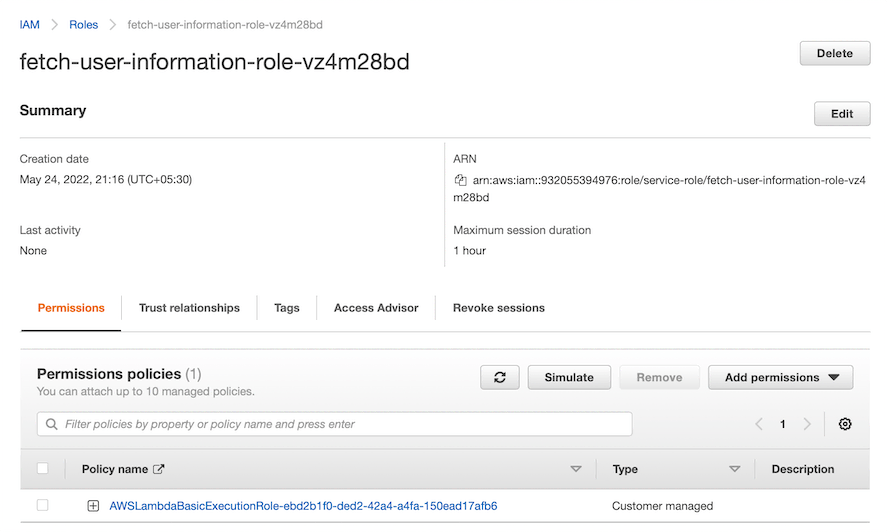
Figure - Viewing the Role bounded to the Lambda function
Afterward, click on "Add Permissions" and select either "Attach Policies" or "Create Inline Policies."
Selecting "Attach Policies"
If you select "Attach Policies," you can choose the DynamoDB policies managed by AWS. Please note that some of these policies provide full access to DynamoDB, giving a Lambda function to perform costly operations such as a "Scan."
The figure shown below highlights the policies for DynamoDB that AWS manages.
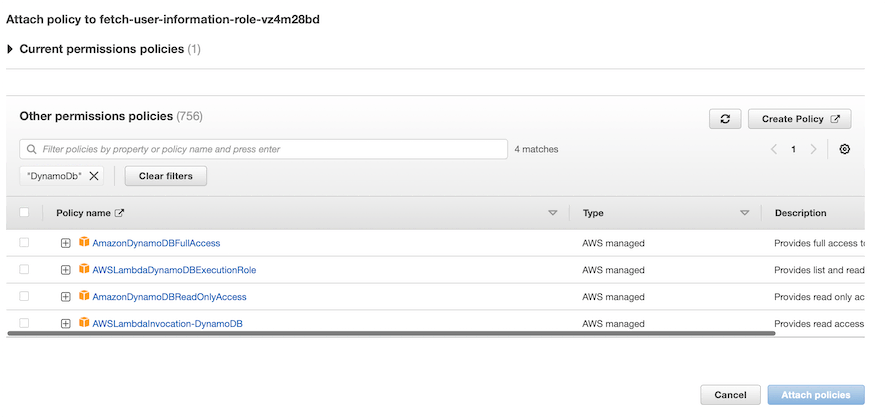
Afterward, you can add the required policies and click "Attach Policies." It may take a few seconds for the policies to attach to the Lambda role.
Then, you can execute DynamoDB operations from the service without any permission error.
Selecting "Create Inline Policies"
However, if you select "Create Inline Policies," you are free to create a custom inline policy with fine-tuned resource access. For example, you can provide a service to only perform a "query" operation and not a "create" operation.
The below figure shows the Create Policy wizard.
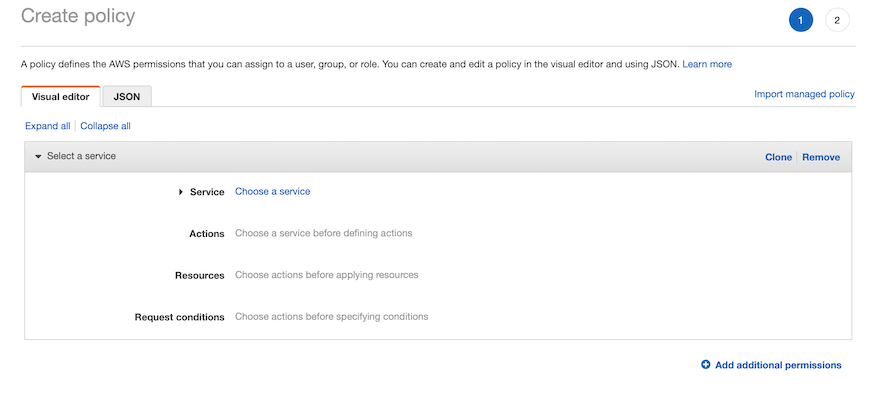
Figure - Creating inline policies.
Using the above wizard, you can provide the "DynamoDB" service and select the actions that the service can execute on the permitted resources (table ARNs).
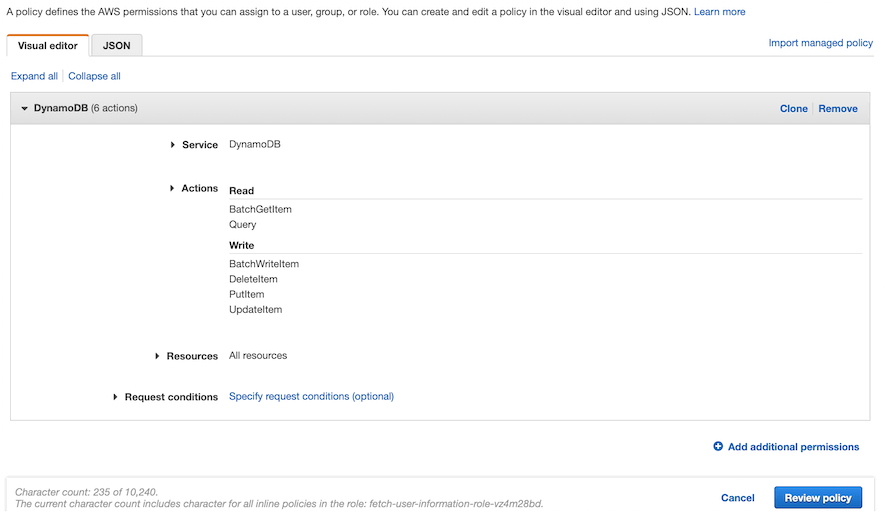
Figure - Defining the custom policy for DynamoDB access
After configuring the authorized actions on the defined resources, click "Review Policy" to review the inline policy.
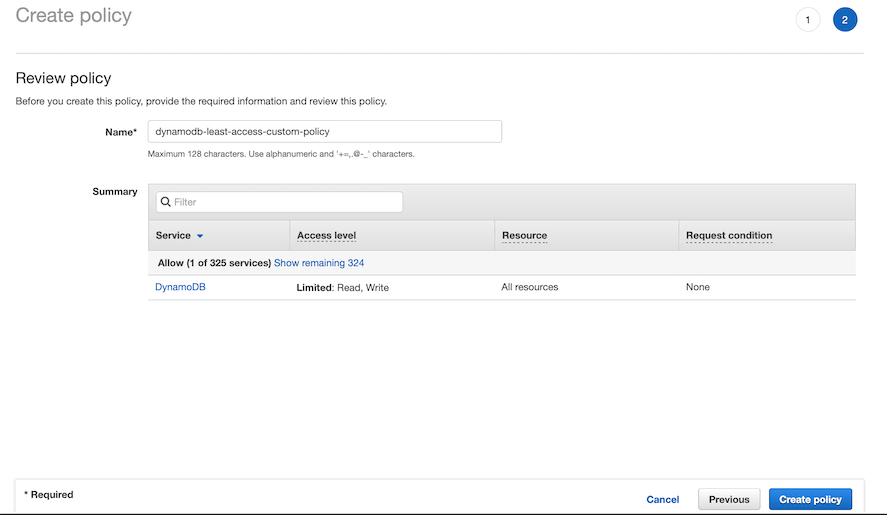
Figure - Reviewing the inline policy
After confirming the permissions, click "Create Policy" to create and bind the policy to the role. With this, developers can implement the principle of least privilege and fine-tune permissions.
Afterward, you can execute the operation in the service, and it will not throw a permissions error.
Other Common DynamoDB Errors (with Solutions)
- dynamodb streams missing events
- dynamodb the parameter cannot be converted to a numeric value NaN
- dynamodb condition does not exist
- dynamodb scan missing values
- dynamodb consistent reads are not supported on global secondary indexes
- can't pickle thread.lock objects typeerror boto3 python dynamodb
- name key is not defined dynamodb
- com amazonaws services dynamodbv2 model resourcenotfoundexception
- DynamoDB ConditionalCheckFailedException
- failed to list tables not authorized dynamodb
- dynamodb global secondary index does not project
- dynamodb-admin command not found
- dynamodb getItem() is not a function
- dynamodb the table does not have the specified index
- ProvisionedThroughputExceededException DynamoDB
Dynobase is a Professional GUI Client for DynamoDB
Start your 7-day free trial today
Product Features
- New in Dynobase 3.0
- Semantic and Vector Search
- Schema Explorer
- Visual JSON Path Filtering
- Visual Item Diff
- MCP Server for AI Tools
- Use SQL with DynamoDB
- Import CSV To DynamoDB
- Import JSON To DynamoDB
- Export DynamoDB To JSON
- Export DynamoDB To S3
- Export DynamoDB To CSV
- DynamoDB Update Item
- DynamoDB Delete All Items
- DynamoDB Delete Item
- DynamoDB Create Table
- DynamoDB Delete Table
- DynamoDB Conditional Update